
Kodem just built the world’s only Dev to Prod Agentic Taskforce in Cyber
AppSec is structurally constrained. Codebases are doubling. Vulnerabilities are compounding. But the number of security engineers capable of triaging, validating, and fixing them is flat, at best.
At RSAC 2025, we launched Kai, the first AI-native application security engineer. Today, we’re expanding it into a fully agentic task force that truly performs AppSec tasks from start to finish.
Kai has evolved from a single agent to a persistent system that scans, manages, and defends applications with the precision and scale that modern environments demand.
The Structural Problem in AppSec
Software release velocity has increased 5–10× over the past decade, driven by microservices, continuous deployment, and open-source adoption. Each deploy potentially exposes a new attack path. Vulnerabilities, especially in dependencies, have scaled alongside.
But AppSec headcount has not.
- Open source is the new default. Snyk data shows that 80–90% of a typical codebase is third-party packages (Snyk, 2023).
- Vulnerability volume is exploding. NVD added over 29,000 CVEs in 2024, and over 60% were tied to libraries or supply chain dependencies.
- Patch cycles are getting slower. Recent research shows median time to remediate critical vulns in large orgs exceeds 120 days (Veracode, 2023).
- Security expertise is lagging. According to ESG (2024), 71% of organizations report an AppSec talent gap.
The result is predictable: growing backlogs, alert fatigue, and long windows of exposure, even in teams with decent tooling.
A Shift in the Market: From CVSS to Exploitability
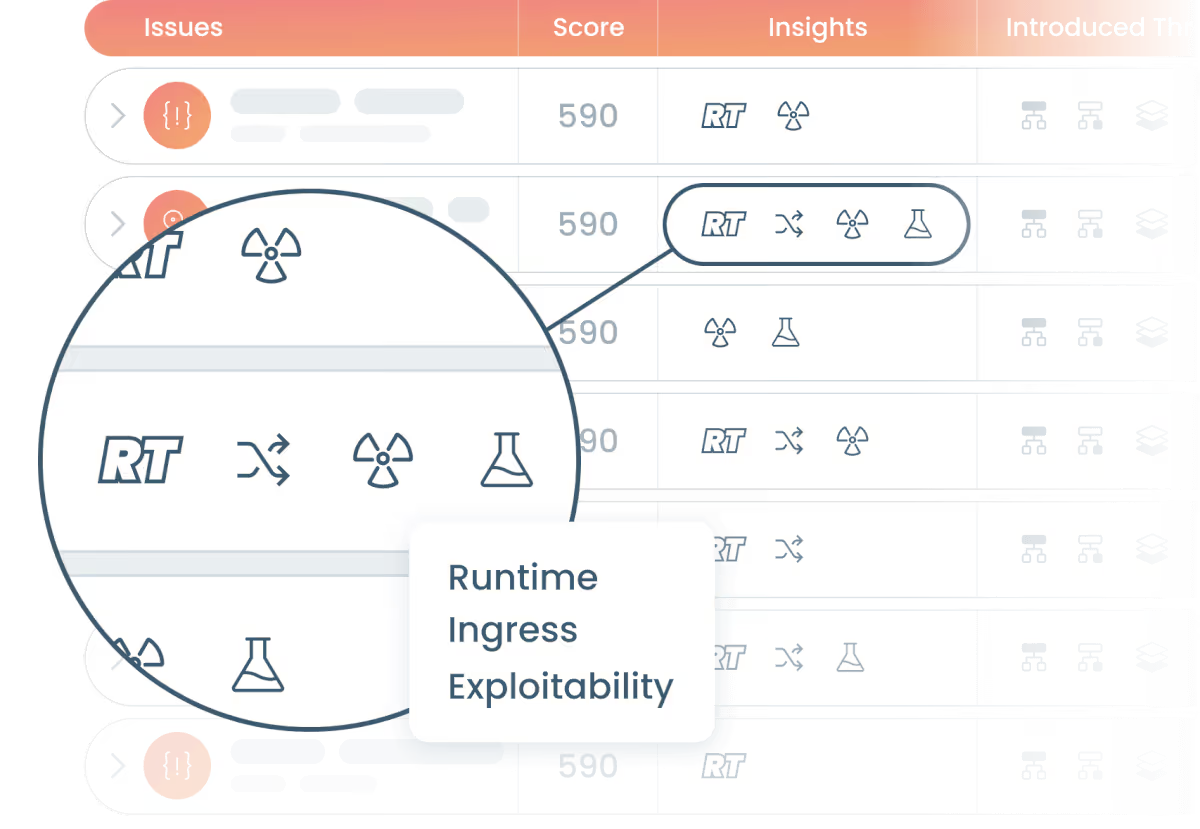
Traditional security tooling prioritizes findings using static CVSS scores. But these do not reflect exploitability in your specific environment.
In 2024 and 2025, multiple signals confirm that the market is now pivoting to reachability, runtime validation, and blast radius.
- FedRAMP CVM RFC 0012: Draft guidelines now explicitly recommend prioritizing vulnerabilities not by CVSS, but by "contextual risk"—including exploitability, reachability, and runtime exposure (FedRAMP, 2024).
- Gartner Hype Cycle for Application Security, 2025: “Reachability Analysis” is highlighted as a high-benefit innovation nearing mainstream adoption. Gartner defines it as “dynamic prioritization using organizational context,” and states that tools that fail to include it will soon be considered outdated (Zumerle et al., 2025).
Practitioners are already there.
“Take the pile of vulnerabilities and make it smaller. That’s the job.”
— Nir Rothenberg, CISO @ Rapyd
“Reachability is about knowing where you’re actually vulnerable.”
— James Berthoty, Kubernetes security researcher
Enter Kai: From Solo Agent to Task Force
Most AI initiatives in security so far are static overlays on static tools: LLMs summarizing scanner output or explaining CWE IDs. Useful, but not scalable.
Kai takes a different approach. It is a multi-agent system built on Kodem’s runtime-aware, eBPF-enabled platform. Each agent solves a specific problem in the AppSec lifecycle. Together, they operate as a persistent force.
What Kai’s Agentic Task Force Can Do
All agents are coordinated via a shared attack map, continuously updated based on code, container, and runtime telemetry.
Why Agentic AI Is the Right Primitive for AppSec
AppSec work is bounded and repeatable:
- Find what matters (scan)
- Confirm it matters (validate)
- Resolve it or escalate (fix/alert)
This pattern is ideal for agents—not general AI assistants.
A monolithic AI cannot reason about blast radius while doing remediation. A task force can. Kai distributes reasoning across specialized agents, enabling parallel action and contextual awareness that static tools lack.
Most importantly, Kai acts. It does not wait for human input to reduce risk.
Early Results
Teams using Kai in design partner programs are seeing measurable outcomes:
- Backlog reduction: One fintech saw their open criticals drop from 1,240 to under 100 in 30 days
- MTTR drop: Median time to remediate reachable vulnerabilities went from 45 days to 4
- Operational overhead: ADR documentation that used to take 2 hours is now fully automated
And when a high-severity memory exploit surfaced in a third-party component, Kai's runtime agent caught it—before a single human alert fired.
What's Next: Meet Kai at Black Hat USA
If the industry is moving away from CVSS and toward attacker-aware prioritization, security teams will need systems that can operate with the same assumptions.
Kai is the only agentic AI task force that scans, manages, and defends applications autonomously.
We’ll be at Black Hat USA here: kodemsecurity.com/events
Meet us for a live demo, technical deep dive, or early access to Kai’s persistent agents.
Join the Kai Waitlist
References
- FedRAMP. (2024). RFC-0012: Continuous Vulnerability Management (CVM) Baseline Guidance. Retrieved from https://www.fedramp.gov/rfcs/0012/
- Gartner. (2025). Hype Cycle for Application Security, 2025 (Zumerle, D., et al.). Gartner, Inc.
- Snyk. (2023). State of Open Source Security. Retrieved from https://snyk.io
- Veracode. (2023). State of Software Security, Volume 12. Retrieved from https://info.veracode.com
- ESG. (2024). The Life and Times of Cybersecurity Professionals. Retrieved from https://www.enterprisestrategygroup.com
{{kai-section="/314695942731"}}
Related blogs
PHP2Shell: CVE-2026-109618 and CVE-2026-109619 Explained
PHP2Shell (CVE-2026-109618, CVE-2026-109619) is unauthenticated PHP RCE in mod_php and PHP-FPM. Get fixed versions, memory_limit mitigations, and the runbook.
14
Stop the waste.
Protect your environment with Kodem.
The State of the Application Security Workflow
This report aims to equip readers with actionable insights that can help future-proof their security programs. Kodem, the publisher of this report, purpose built a platform that bridges these gaps by unifying shift-left strategies with runtime monitoring and protection.
Get real-time insights across the full stack…code, containers, OS, and memory
Watch how Kodem’s runtime security platform detects and blocks attacks before they cause damage. No guesswork. Just precise, automated protection.