Kodem puts frontier reasoning inside the runtime security system that discovers, governs, protects, and responds across applications and the AI agents inside them.
TEL AVIV, September 22, 2026. Kodem Security, the runtime-powered application intelligence company, today announced it has been accepted into OpenAI's Daybreak Cyber Partner Program, which gives approved defenders governed access to OpenAI's frontier cybersecurity models.
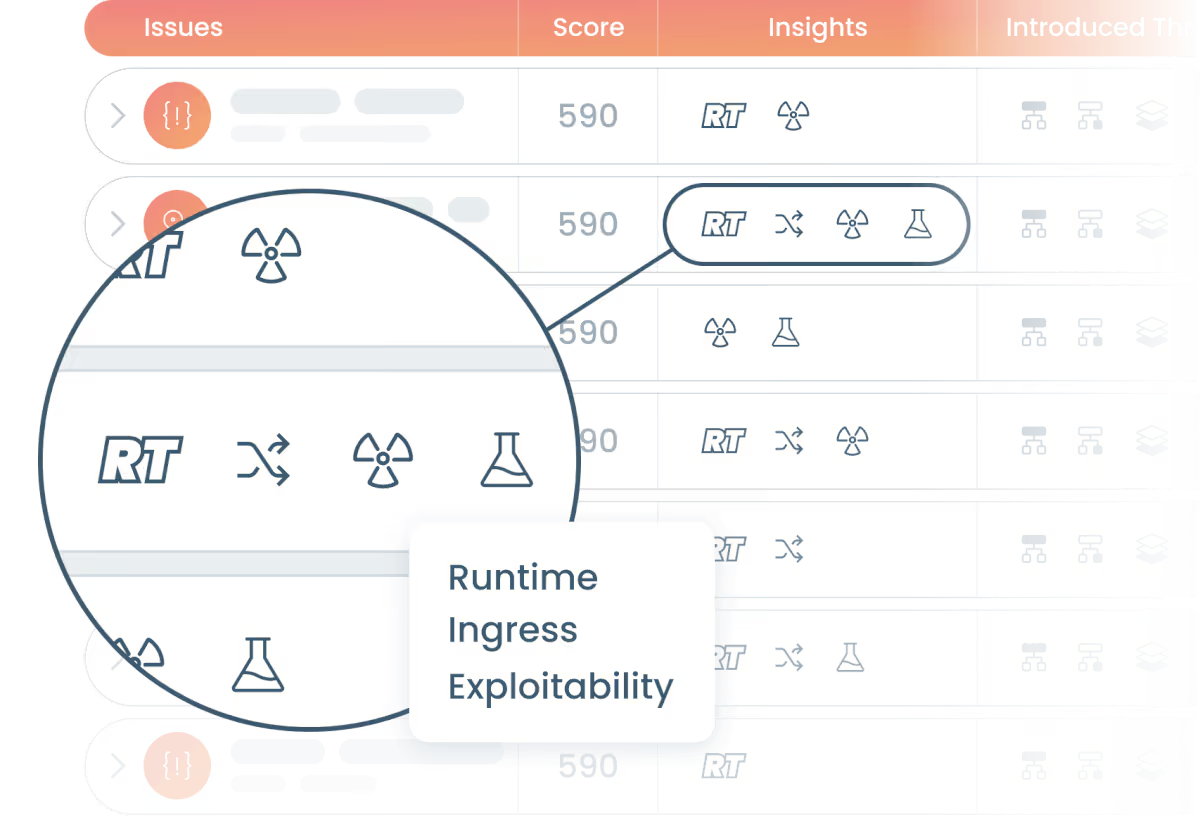
Frontier models can now find vulnerabilities, test patches, and reason about exploitability at machine speed. Kodem is the system that turns that reasoning into outcomes in production. Its platform reads applications and the AI agents inside them from runtime, discovers every package, function, agent, tool, MCP server, model, and guardrail as loaded, governs each agent by identity, protects with scoped and reversible controls, detects and responds to what moves in production, and verifies the result. Daybreak makes the reasoning inside that loop stronger.
"Finding bugs is no longer the hard part. Acting on them safely in production is," said Aviv Mussinger, co-founder and CEO of Kodem Security. "Daybreak puts a stronger reasoning engine in defenders' hands. Kodem is the system that engine runs inside: it sees the application, governs the agents, protects the workload, and proves the fix. The model thinks faster. Kodem sees, decides, acts, and proves."
Runtime AI security for the agentic application layer
Applications are now written, extended, and executed by AI agents. A tool can be registered at runtime that no code review saw. A guardrail can be switched on in a console and never loaded in the process. Kodem's AI Security capabilities reconstruct every agent, workflow, tool, model, and guardrail from memory, map the data each agent can reach and where that data can go, and attribute each action to the agent that originated it. On that foundation Kodem governs each agent with its own policy, enforces at the AI gateway and in the workload, detects and responds through application detection and response (ADR), and verifies every change. Each control is validated before enforcement, scoped, reversible, and approved by the customer.
"Customers do not need another list of what might be wrong. They need the agent that picked up a refund tool nobody asked for found, governed, and stopped before it fires - and proof it stays closed. Kodem does that at runtime today. Daybreak puts frontier reasoning inside that loop from day one," said Mahesh Babu, CISO (Field) at Kodem Security.
How Kodem will use the access
Kodem will apply the Daybreak models across its runtime loop: validating exploitability against loaded state, sharpening per-agent governance decisions, and driving detection and response in production, beginning inside Kodem's own workloads. Model access is scoped and logged, runs against Kodem environments first, and keeps customer data out of scope unless a customer opts in. Kodem will share what it learns with the security community as the work matures.
"Our sensors read the process, not the manifest," said Pavel Furman, co-founder and CTO of Kodem Security. "That is what lets us govern an agent by who it is, protect one workload without touching the next, and respond to what is actually happening. A model built to reason about exploitability makes every one of those decisions sharper."
To learn more, visit Runtime AI Security, Application Detection and Response, and runtime intelligence.
About Kodem Security
Kodem Security is the runtime-powered application intelligence platform. Founded in 2021 and headquartered in Tel Aviv, Kodem gives security and engineering teams one system that discovers what their applications and AI agents actually load, execute, and reach in production, governs and protects them, and detects, responds, and verifies when something moves. Kodem is trusted by dozens of customers across financial services, technology, and critical industries. Learn more at kodemsecurity.com.
Media contact
Mahesh Babu
[email protected]
Related blogs

Introducing Runtime Application Defense for WAF Environments
Turning perimeter security into full-spectrum application defense
3

Kodem Security Joins the GKE Autopilot Partner Ecosystem
Kodem Security is now an approved GKE Autopilot Partner, enabling its runtime-first application security platform to deploy natively in Autopilot clusters.
How Rapyd Used Kodem to Shift from Volume to Impact
Rapyd, a global fintech platform operating in over 100 countries, partnered with Kodem to modernize its application security program. Faced with mounting vulnerabilities and a shortage of specialized AppSec talent, Rapyd needed more than another scanner—it needed a platform that could think like an expert. Kodem delivered measurable reductions in triage time, rework, and risk exposure by focusing on what attackers can actually exploit.
Stop the waste.
Protect your environment with Kodem.
The State of the Application Security Workflow
This report aims to equip readers with actionable insights that can help future-proof their security programs. Kodem, the publisher of this report, purpose built a platform that bridges these gaps by unifying shift-left strategies with runtime monitoring and protection.

Get real-time insights across the full stack…code, containers, OS, and memory
Watch how Kodem’s runtime security platform detects and blocks attacks before they cause damage. No guesswork. Just precise, automated protection.